Celebrating 27 Years

Celebrating 27 Years – Announcing the new GeoTrust Horizon® platform. Learn More

GEOTRUST RESEARCH · OCTOBER 2026 CRAWL

The State of SSL/TLS

We used GeoTrust SSL Monitor to analyze the security of the world's 1,000,000 most-visited websites.

INDUSTRY
  • All industries1,000,000
  • Adult25,205
  • Cloud & Infrastructure53,759
  • E-commerce & Retail153,639
  • Education104,381
  • Finance34,943
  • Gaming & Gambling91,102
  • Government22,430
  • Healthcare43,301
  • Media & Social122,588
  • News & Publishing34,946
  • Software & Internet234,505
  • Telecom7,357
  • Travel & Local59,026
  • Other12,818
REGION
  • All regions1,000,000
  • North America151,666
  • South America36,166
  • Europe261,572
  • Asia180,128
  • Middle East23,626
  • Africa11,295
  • Oceania14,128
  • Unknown321,408
RANK
  • All ranks1,000,000
  • top 1k781
  • 1k–10k7,514
  • 10k–100k77,557
  • 100k+914,148

Showing 1,000,000 of 1,000,000 websites

Compliance lens

Conformance with federal, PCI and NIST TLS requirements

How well do websites meet government security requirements?

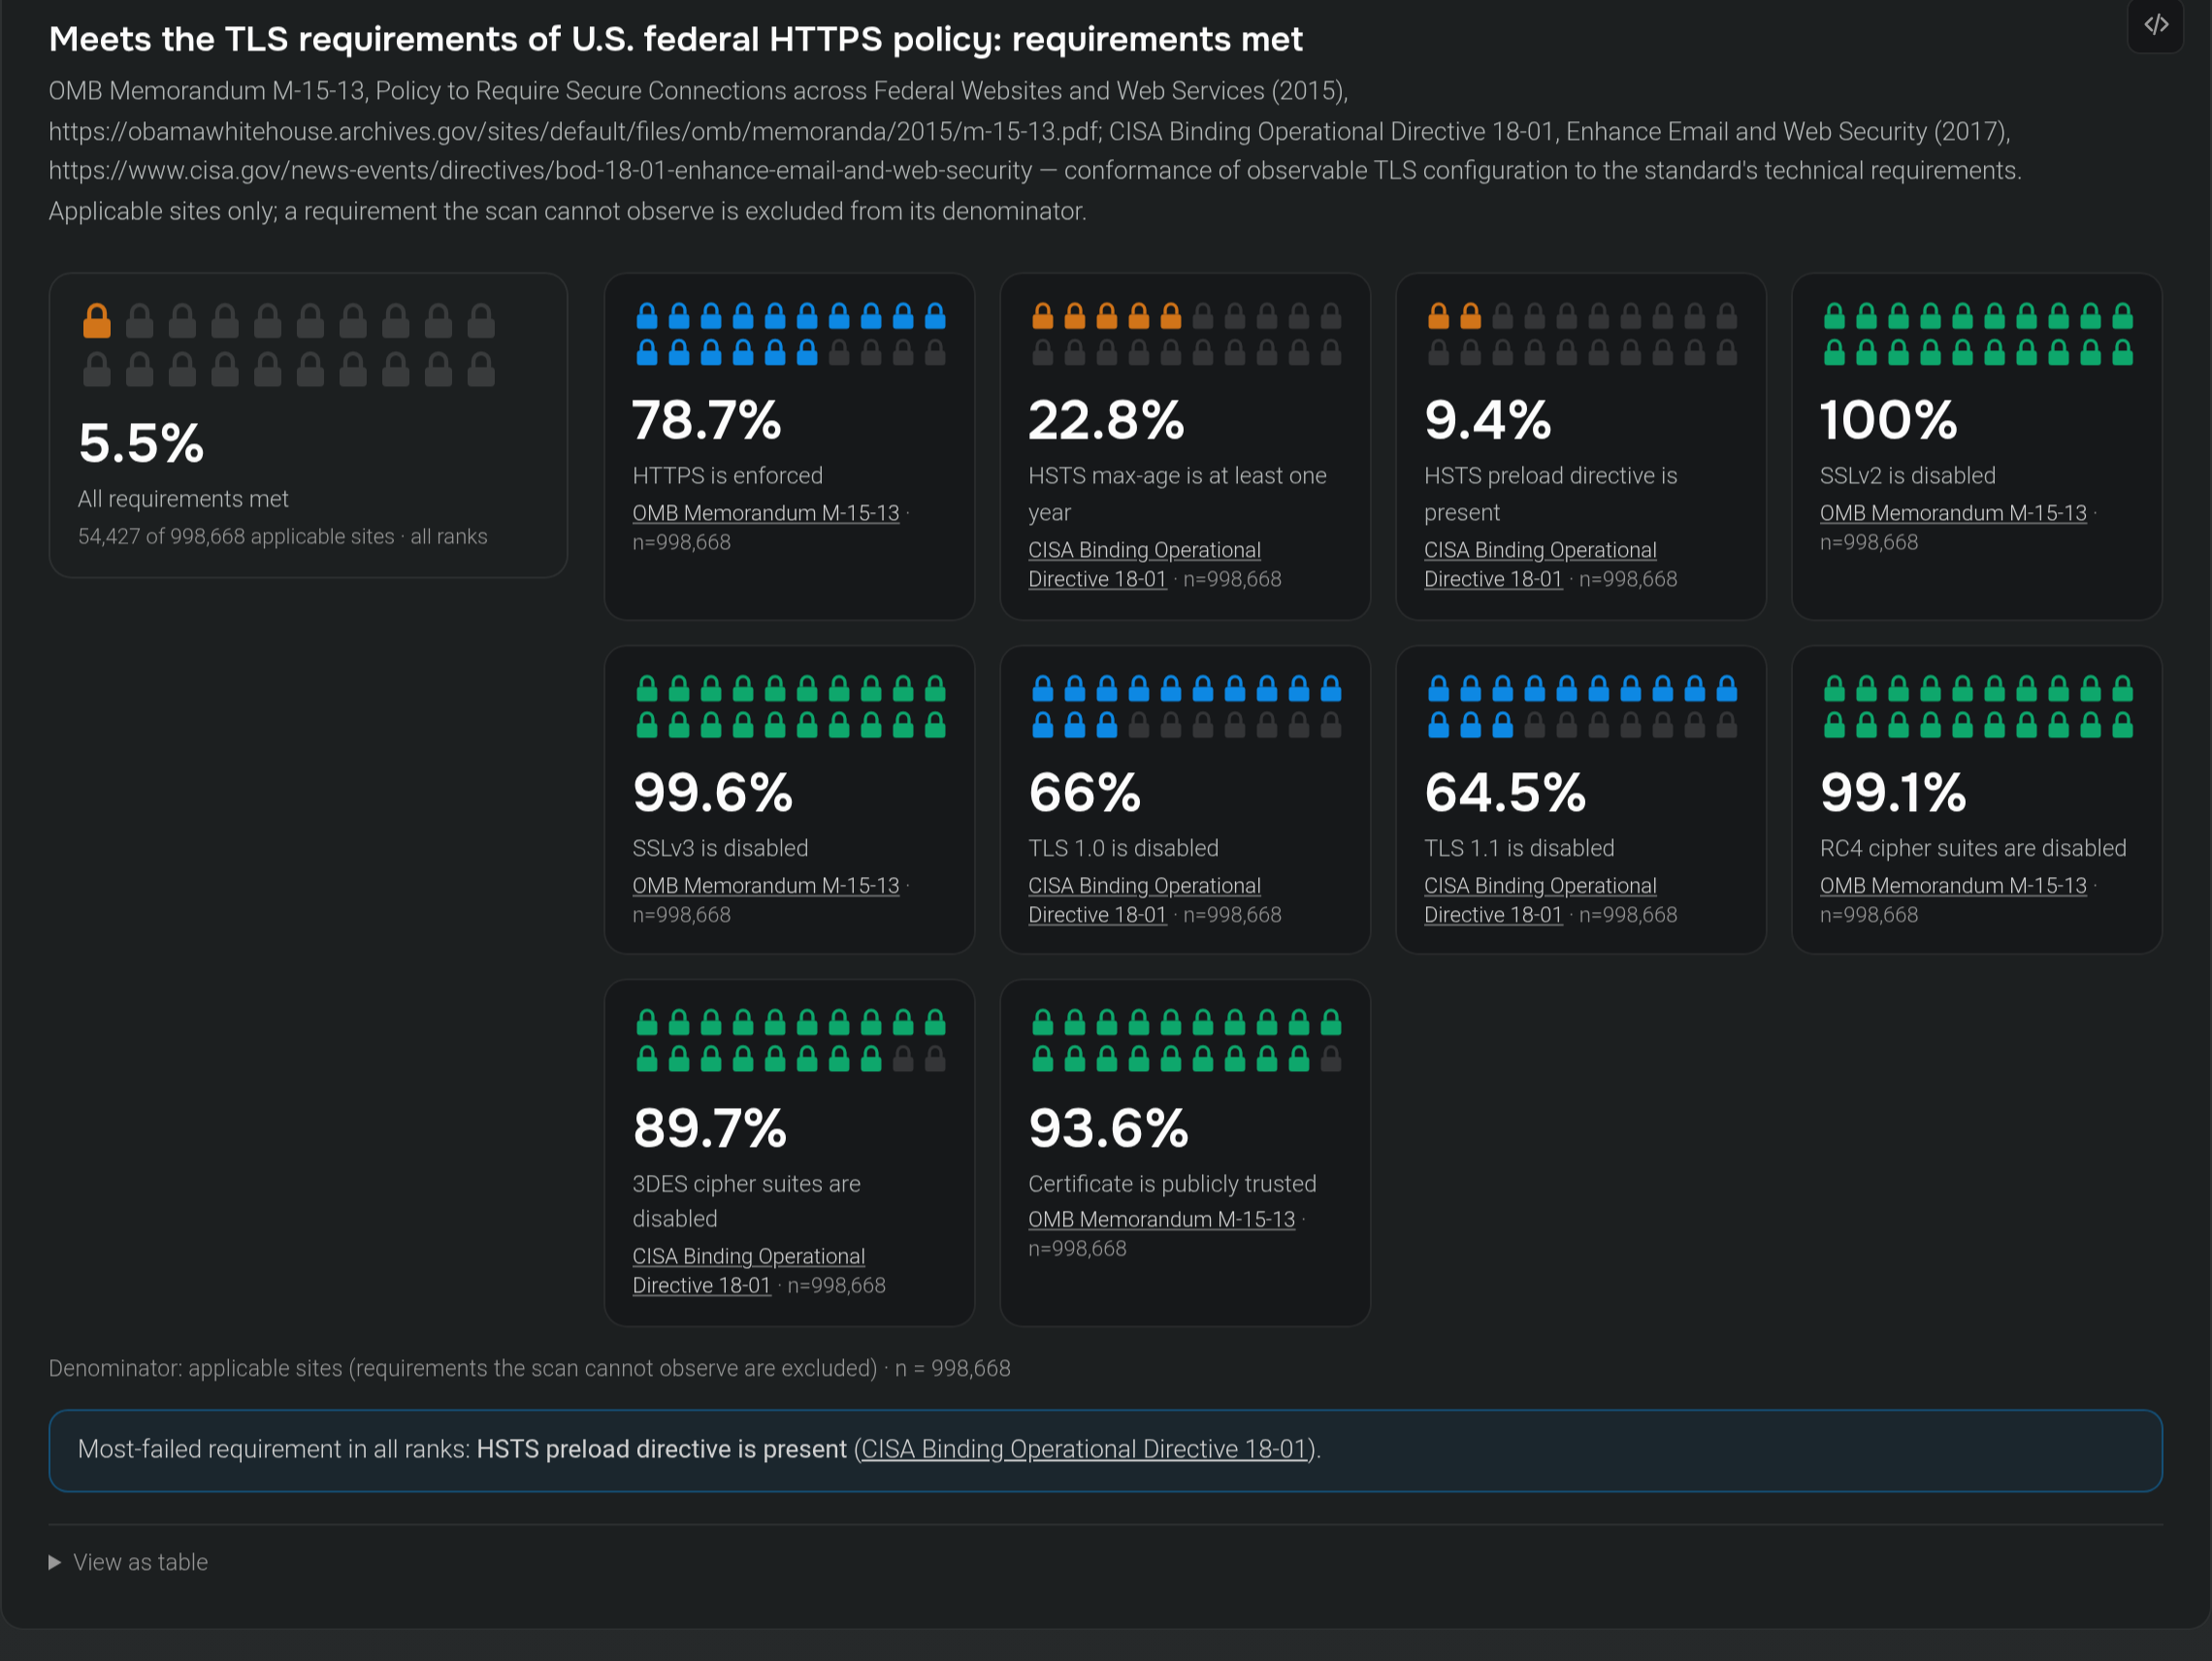
Meets the TLS requirements of U.S. federal HTTPS policy: requirements met

OMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf; CISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security — conformance of observable TLS configuration to the standard's technical requirements. Applicable sites only; a requirement the scan cannot observe is excluded from its denominator.

All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% All requirements met: 5.5% 5.5%All requirements met54,427 of 998,668 applicable sites · all ranks
HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% HTTPS is enforced: 78.7% 78.7%HTTPS is enforcedOMB Memorandum M-15-13 · n=998,668
HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% HSTS max-age is at least one year: 22.8% 22.8%HSTS max-age is at least one yearCISA Binding Operational Directive 18-01 · n=998,668
HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% HSTS preload directive is present: 9.4% 9.4%HSTS preload directive is presentCISA Binding Operational Directive 18-01 · n=998,668
SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% SSLv2 is disabled: 100% 100%SSLv2 is disabledOMB Memorandum M-15-13 · n=998,668
SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% SSLv3 is disabled: 99.6% 99.6%SSLv3 is disabledOMB Memorandum M-15-13 · n=998,668
TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% TLS 1.0 is disabled: 66% 66%TLS 1.0 is disabledCISA Binding Operational Directive 18-01 · n=998,668
TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% TLS 1.1 is disabled: 64.5% 64.5%TLS 1.1 is disabledCISA Binding Operational Directive 18-01 · n=998,668
RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% RC4 cipher suites are disabled: 99.1% 99.1%RC4 cipher suites are disabledOMB Memorandum M-15-13 · n=998,668
3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 3DES cipher suites are disabled: 89.7% 89.7%3DES cipher suites are disabledCISA Binding Operational Directive 18-01 · n=998,668
Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% Certificate is publicly trusted: 93.6% 93.6%Certificate is publicly trustedOMB Memorandum M-15-13 · n=998,668

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n = 998,668

Most-failed requirement in all ranks: HSTS preload directive is present (CISA Binding Operational Directive 18-01).

View as table
RequirementCitationPass sharen
All requirementsOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf; CISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security5.5%998,668
HTTPS is enforcedOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf78.7%998,668
HSTS max-age is at least one yearCISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security22.8%998,668
HSTS preload directive is presentCISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security9.4%998,668
SSLv2 is disabledOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf100%998,668
SSLv3 is disabledOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf99.6%998,668
TLS 1.0 is disabledCISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security66%998,668
TLS 1.1 is disabledCISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security64.5%998,668
RC4 cipher suites are disabledOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf99.1%998,668
3DES cipher suites are disabledCISA Binding Operational Directive 18-01, Enhance Email and Web Security (2017), https://www.cisa.gov/news-events/directives/bod-18-01-enhance-email-and-web-security89.7%998,668
Certificate is publicly trustedOMB Memorandum M-15-13, Policy to Require Secure Connections across Federal Websites and Web Services (2015), https://obamawhitehouse.archives.gov/sites/default/files/omb/memoranda/2015/m-15-13.pdf93.6%998,668

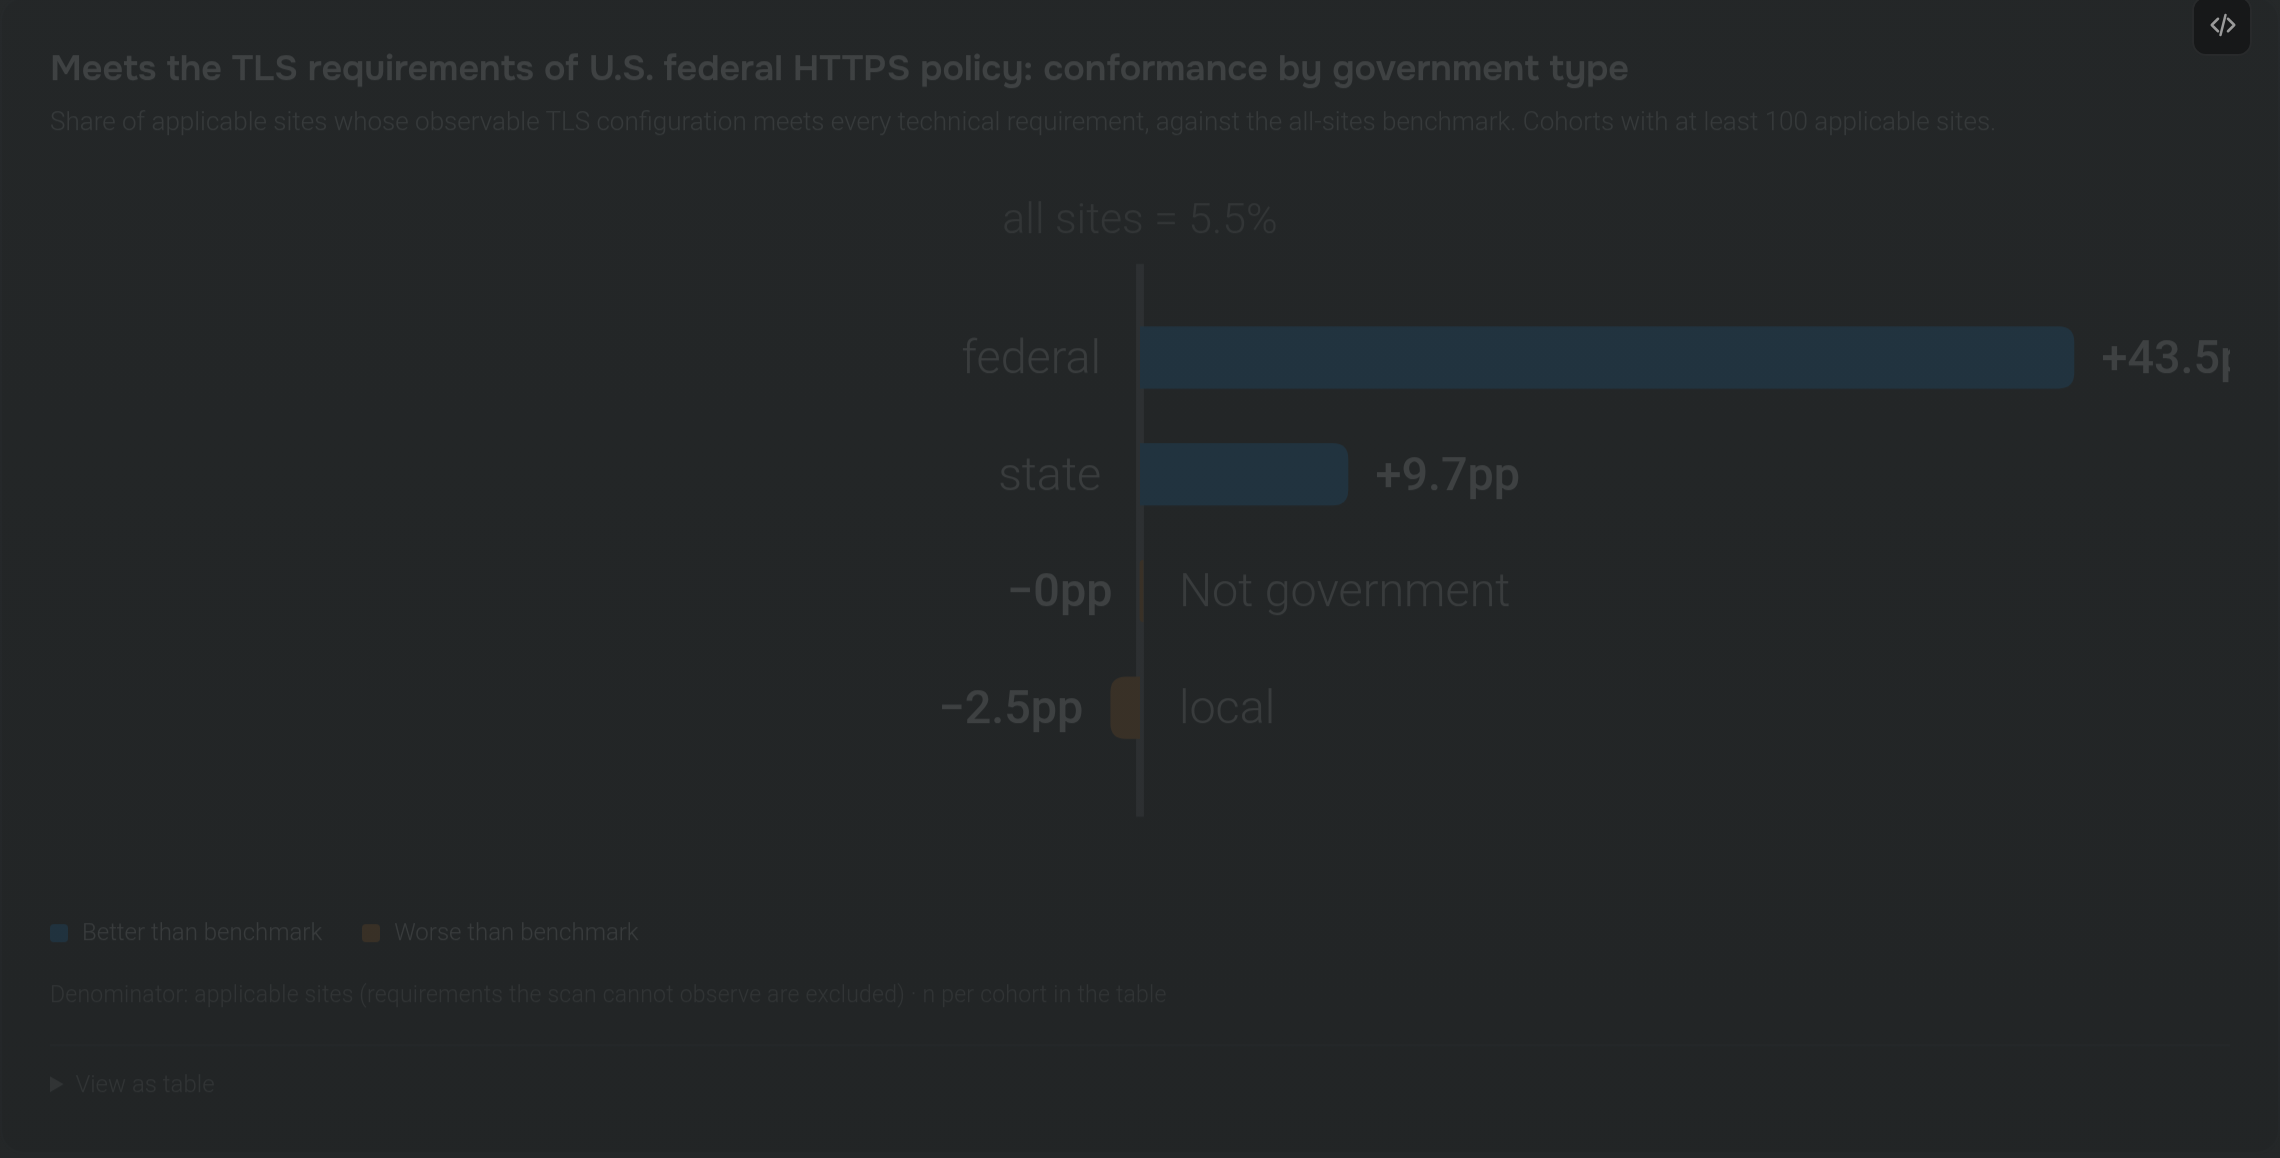
Meets the TLS requirements of U.S. federal HTTPS policy: conformance by government type

Share of applicable sites whose observable TLS configuration meets every technical requirement, against the all-sites benchmark. Cohorts with at least 100 applicable sites.

all sites = 5.5%federal: 49; +43.5pp vs all sites = 5.5% (better); n=533 federal +43.5ppstate: 15.2; +9.7pp vs all sites = 5.5% (better); n=330 state +9.7ppNot government: 5.4; −0pp vs all sites = 5.5% (worse); n=996730 Not government −0pplocal: 2.9; −2.5pp vs all sites = 5.5% (worse); n=1061 local −2.5pp
Better than benchmarkWorse than benchmark

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n per cohort in the table

View as table
govTypeAll requirements metMost-failed requirementn
federal49%HSTS preload directive is present533
state15.2%HSTS preload directive is present330
Not government5.4%HSTS preload directive is present996,730
local2.9%HSTS preload directive is present1,061

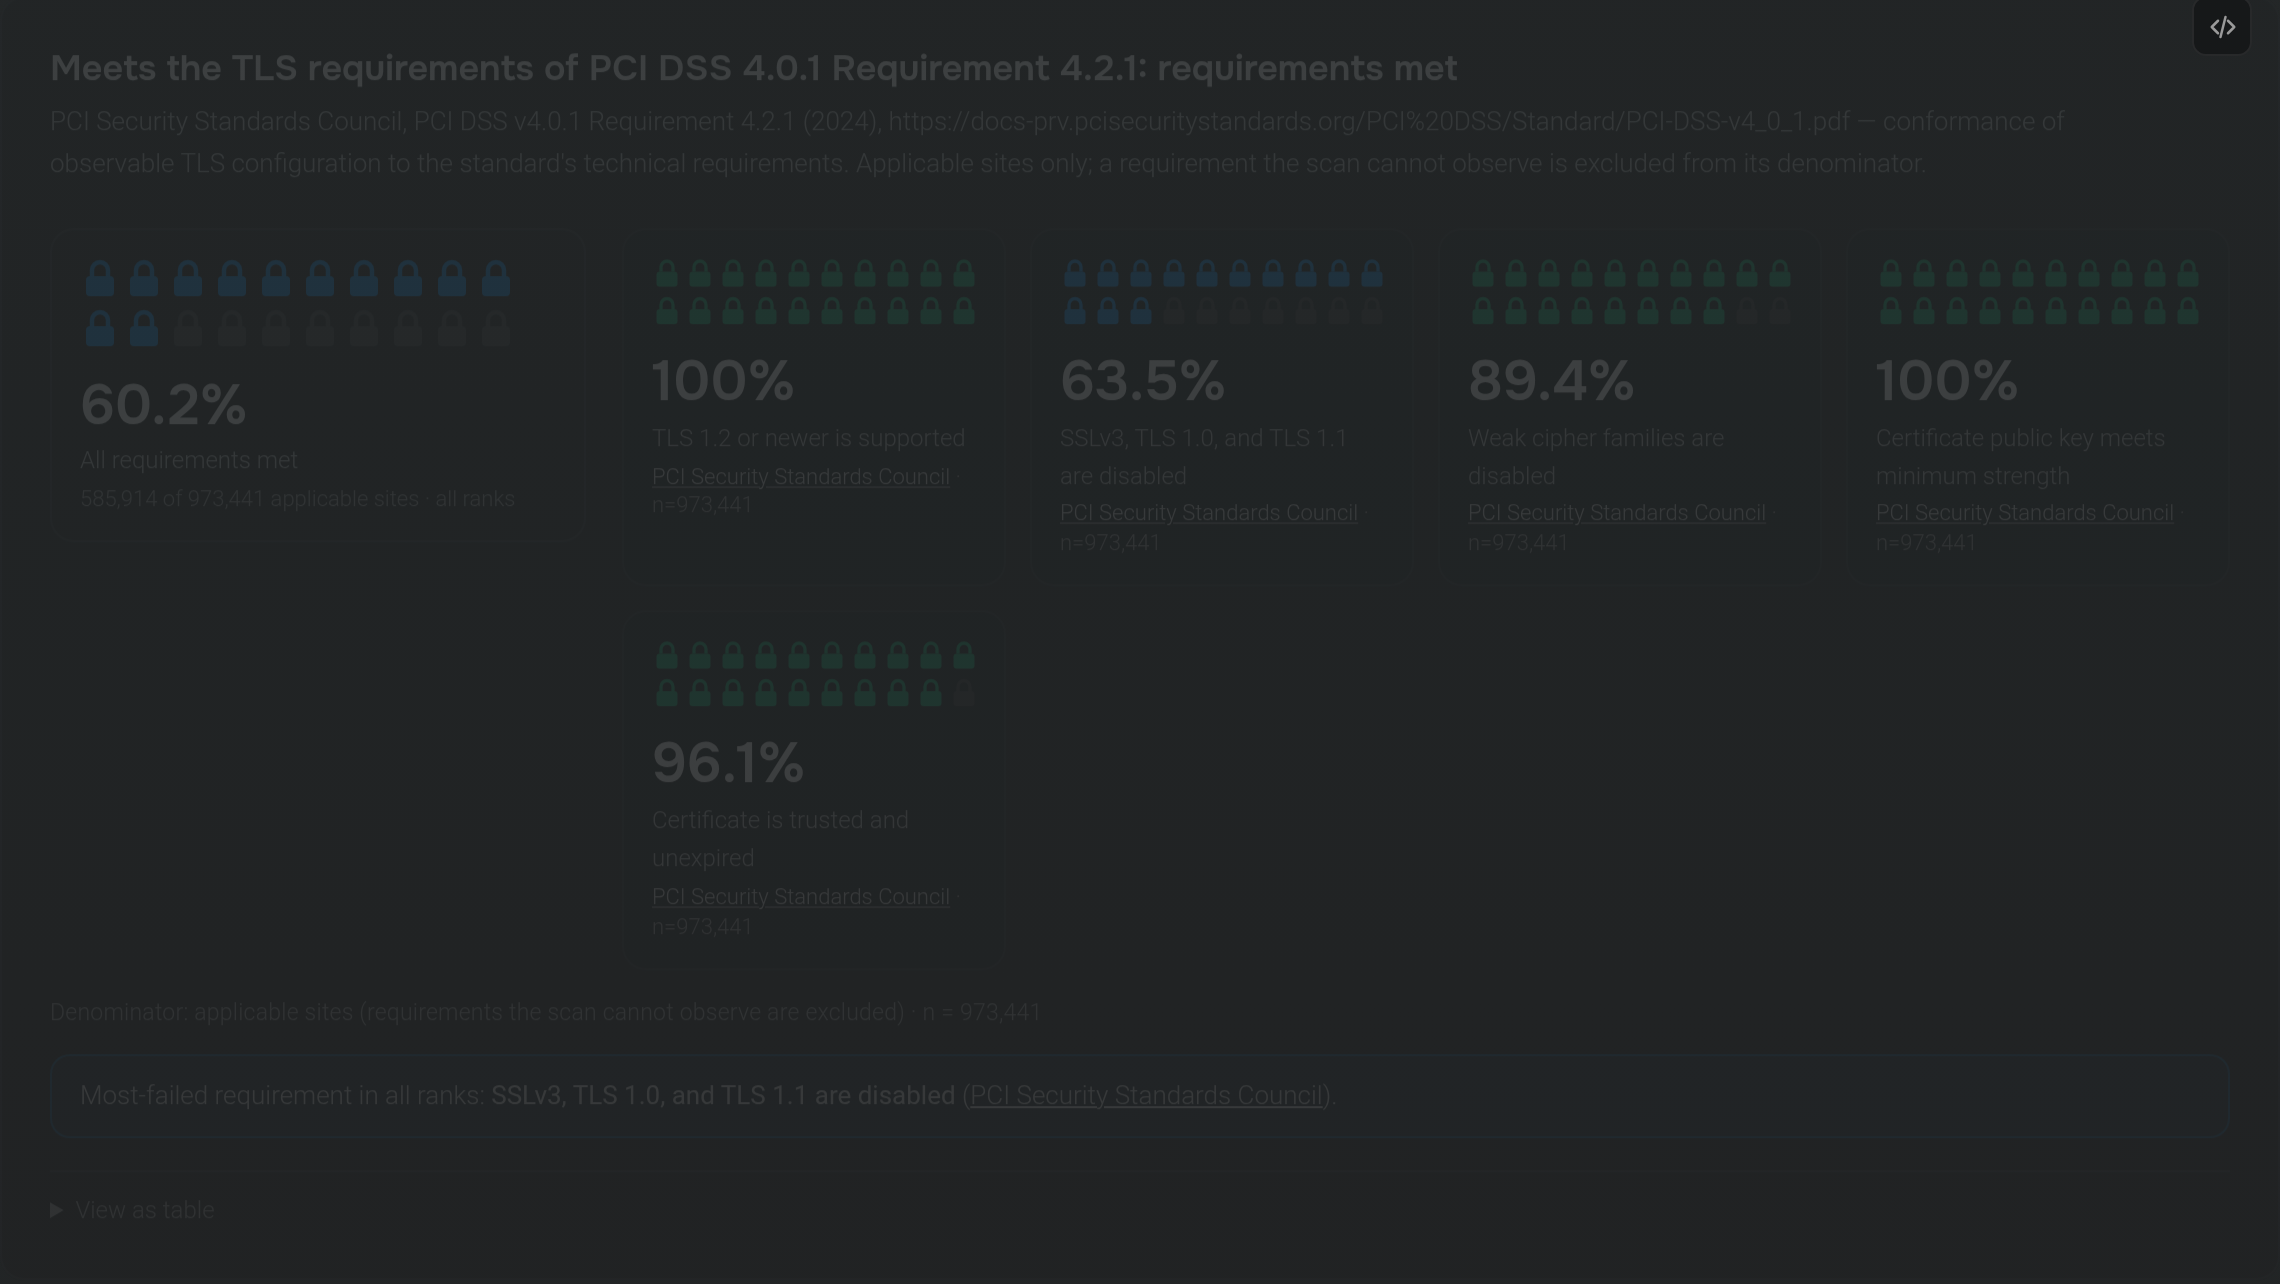
Meets the TLS requirements of PCI DSS 4.0.1 Requirement 4.2.1: requirements met

PCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf — conformance of observable TLS configuration to the standard's technical requirements. Applicable sites only; a requirement the scan cannot observe is excluded from its denominator.

All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% All requirements met: 60.2% 60.2%All requirements met585,914 of 973,441 applicable sites · all ranks
TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% TLS 1.2 or newer is supported: 100% 100%TLS 1.2 or newer is supportedPCI Security Standards Council · n=973,441
SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% 63.5%SSLv3, TLS 1.0, and TLS 1.1 are disabledPCI Security Standards Council · n=973,441
Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% Weak cipher families are disabled: 89.4% 89.4%Weak cipher families are disabledPCI Security Standards Council · n=973,441
Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% 100%Certificate public key meets minimum strengthPCI Security Standards Council · n=973,441
Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% Certificate is trusted and unexpired: 96.1% 96.1%Certificate is trusted and unexpiredPCI Security Standards Council · n=973,441

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n = 973,441

Most-failed requirement in all ranks: SSLv3, TLS 1.0, and TLS 1.1 are disabled (PCI Security Standards Council).

View as table
RequirementCitationPass sharen
All requirementsPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf60.2%973,441
TLS 1.2 or newer is supportedPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf100%973,441
SSLv3, TLS 1.0, and TLS 1.1 are disabledPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf63.5%973,441
Weak cipher families are disabledPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf89.4%973,441
Certificate public key meets minimum strengthPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf100%973,441
Certificate is trusted and unexpiredPCI Security Standards Council, PCI DSS v4.0.1 Requirement 4.2.1 (2024), https://docs-prv.pcisecuritystandards.org/PCI%20DSS/Standard/PCI-DSS-v4_0_1.pdf96.1%973,441

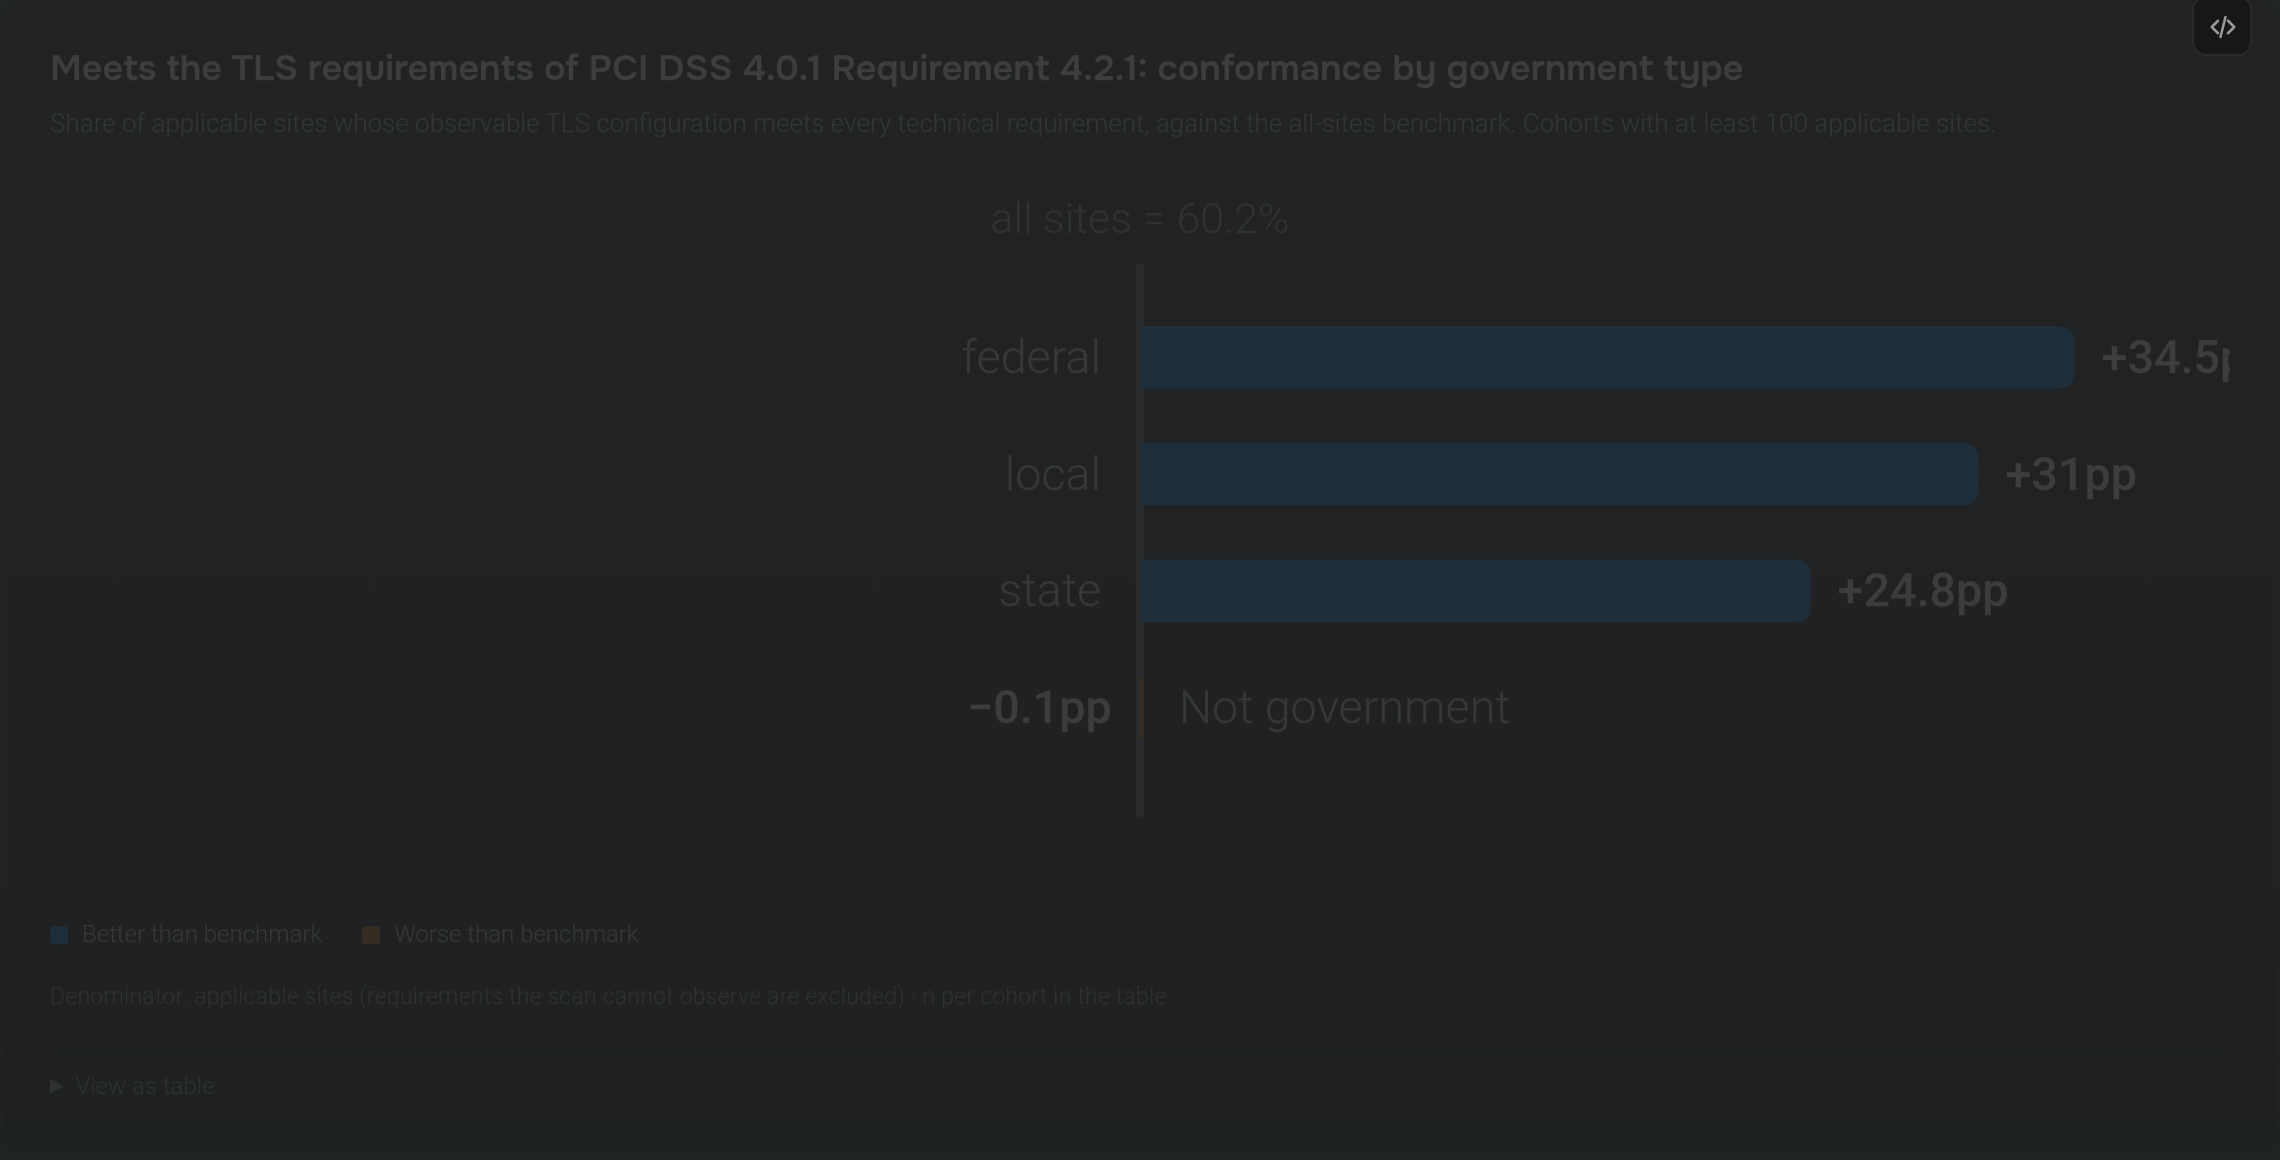
Meets the TLS requirements of PCI DSS 4.0.1 Requirement 4.2.1: conformance by government type

Share of applicable sites whose observable TLS configuration meets every technical requirement, against the all-sites benchmark. Cohorts with at least 100 applicable sites.

all sites = 60.2%federal: 94.7; +34.5pp vs all sites = 60.2% (better); n=531 federal +34.5pplocal: 91.2; +31pp vs all sites = 60.2% (better); n=1055 local +31ppstate: 85; +24.8pp vs all sites = 60.2% (better); n=326 state +24.8ppNot government: 60.1; −0.1pp vs all sites = 60.2% (worse); n=971515 Not government −0.1pp
Better than benchmarkWorse than benchmark

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n per cohort in the table

View as table
govTypeAll requirements metMost-failed requirementn
federal94.7%SSLv3, TLS 1.0, and TLS 1.1 are disabled531
local91.2%SSLv3, TLS 1.0, and TLS 1.1 are disabled1,055
state85%SSLv3, TLS 1.0, and TLS 1.1 are disabled326
Not government60.1%SSLv3, TLS 1.0, and TLS 1.1 are disabled971,515

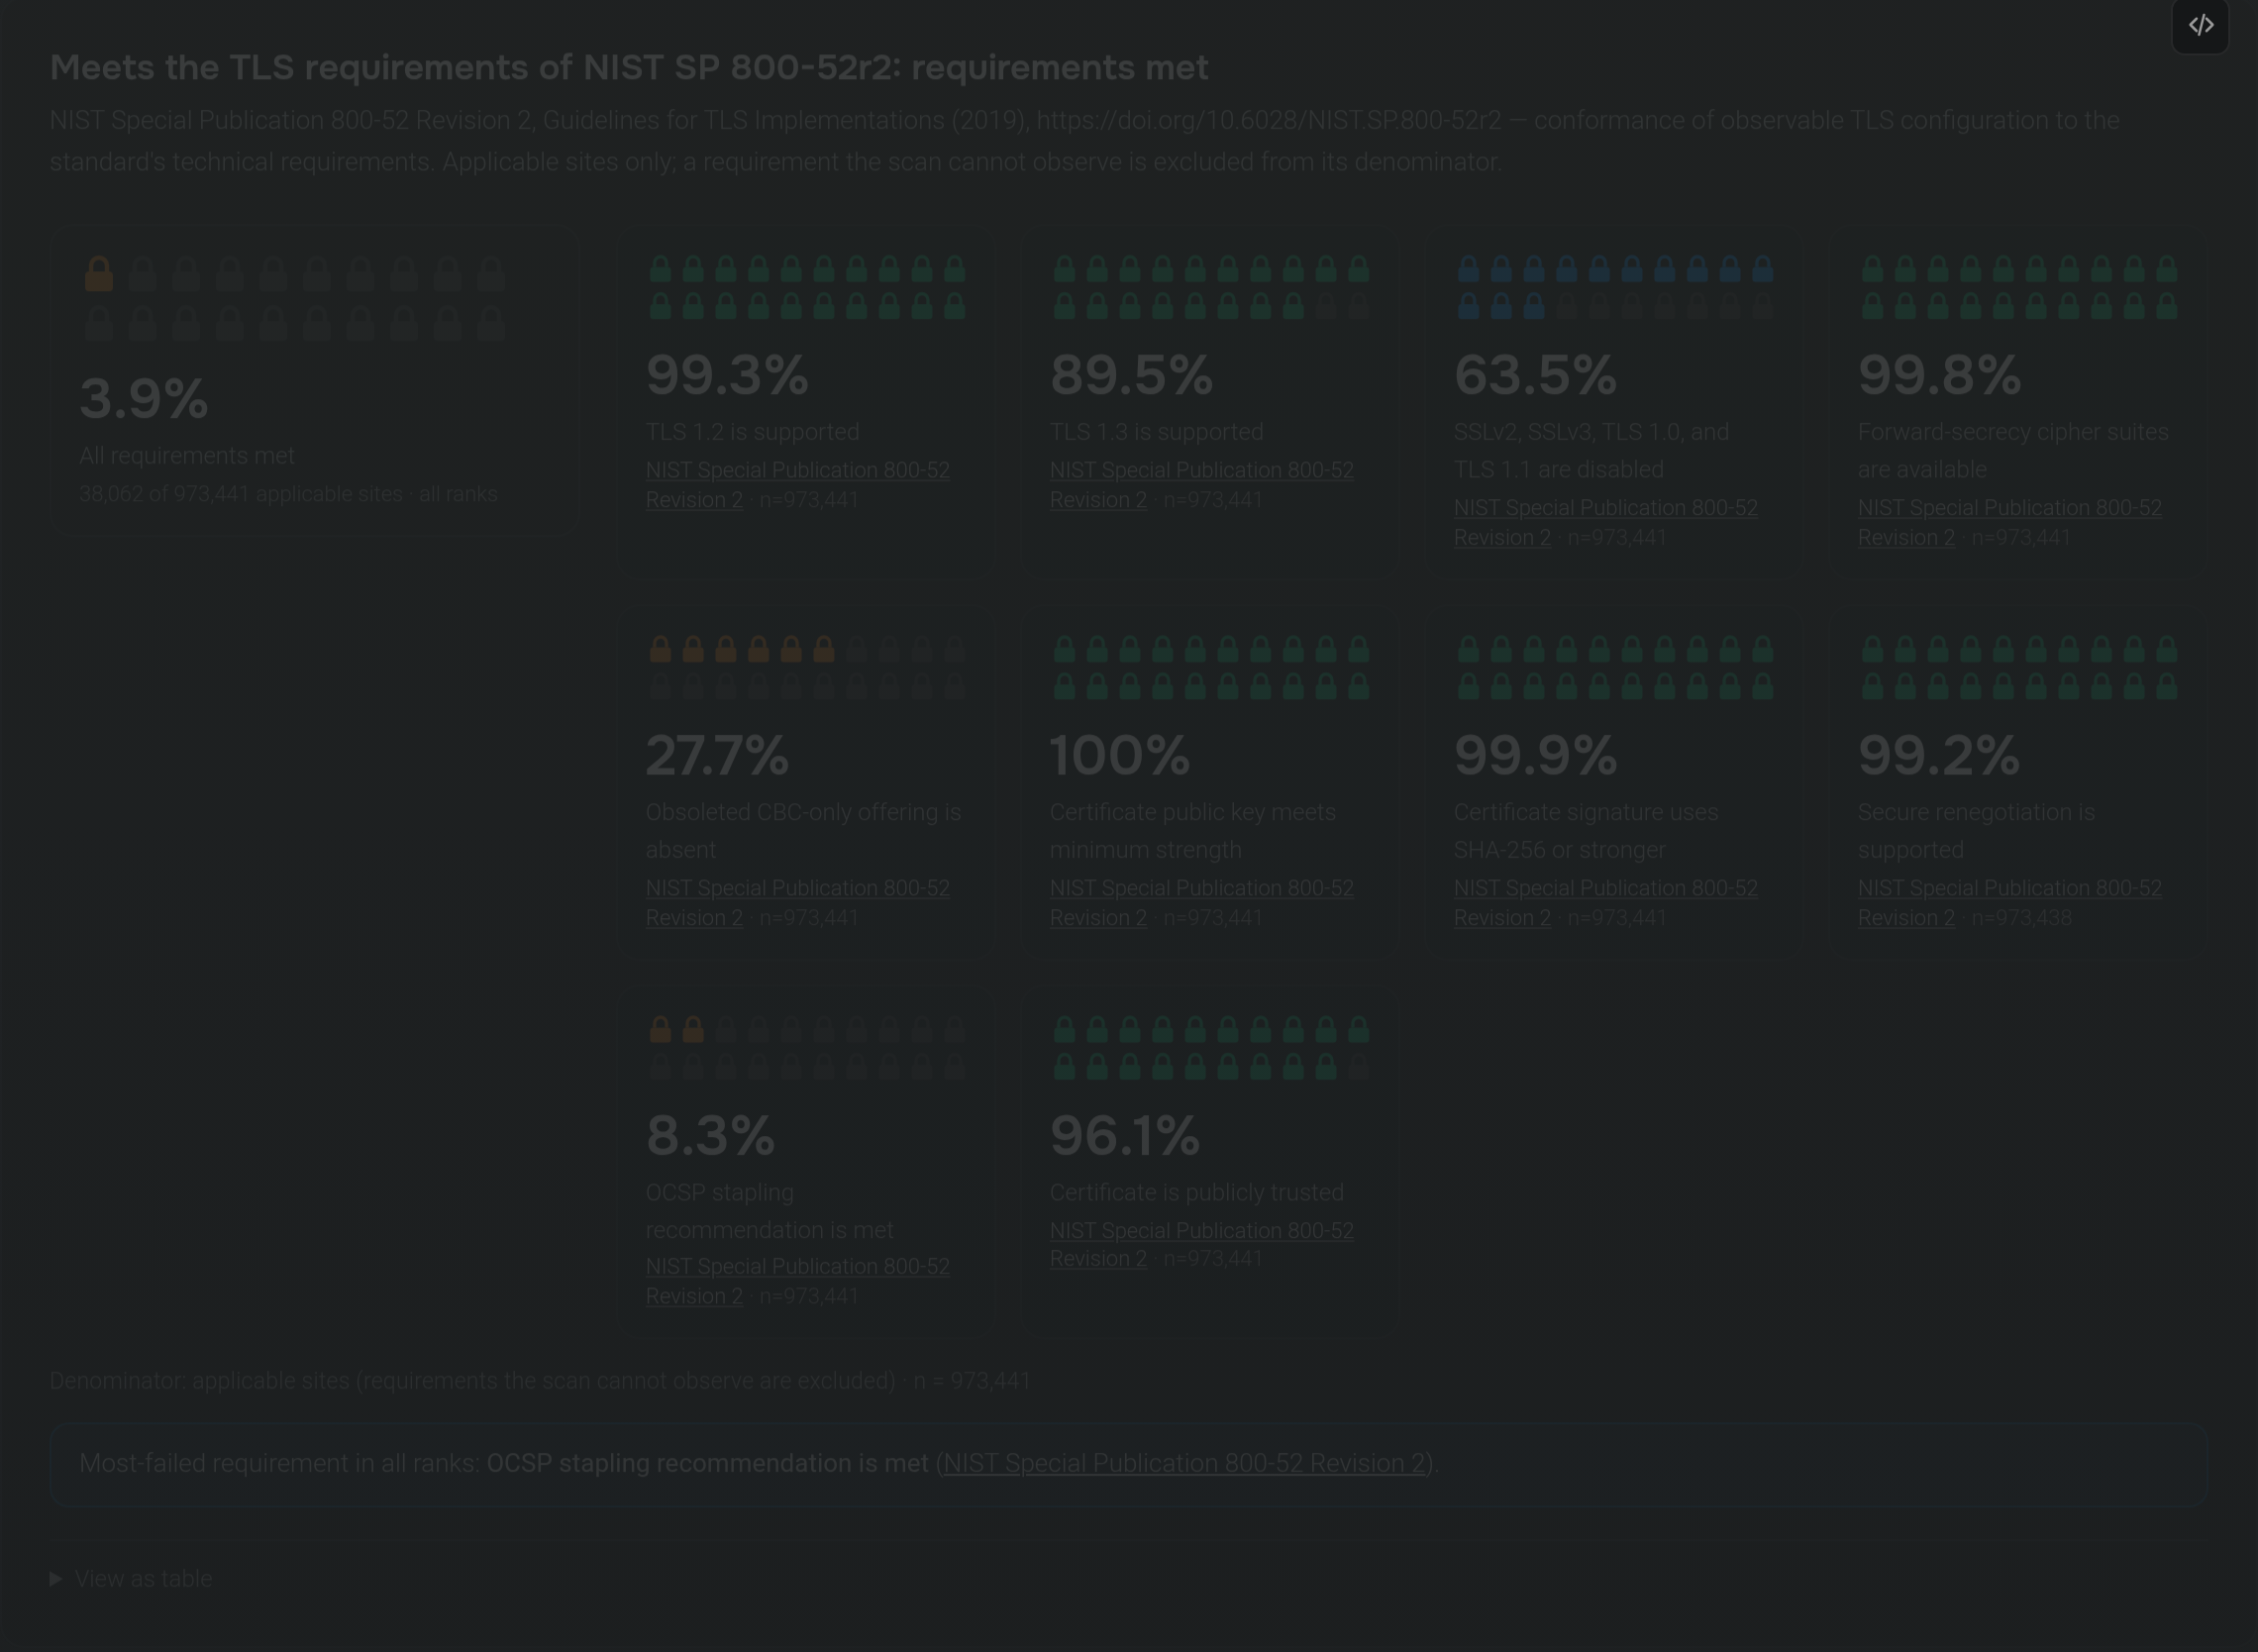
Meets the TLS requirements of NIST SP 800-52r2: requirements met

NIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r2 — conformance of observable TLS configuration to the standard's technical requirements. Applicable sites only; a requirement the scan cannot observe is excluded from its denominator.

All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% All requirements met: 3.9% 3.9%All requirements met38,062 of 973,441 applicable sites · all ranks
TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% TLS 1.2 is supported: 99.3% 99.3%TLS 1.2 is supportedNIST Special Publication 800-52 Revision 2 · n=973,441
TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% TLS 1.3 is supported: 89.5% 89.5%TLS 1.3 is supportedNIST Special Publication 800-52 Revision 2 · n=973,441
SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabled: 63.5% 63.5%SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabledNIST Special Publication 800-52 Revision 2 · n=973,441
Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% Forward-secrecy cipher suites are available: 99.8% 99.8%Forward-secrecy cipher suites are availableNIST Special Publication 800-52 Revision 2 · n=973,441
Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% Obsoleted CBC-only offering is absent: 27.7% 27.7%Obsoleted CBC-only offering is absentNIST Special Publication 800-52 Revision 2 · n=973,441
Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% Certificate public key meets minimum strength: 100% 100%Certificate public key meets minimum strengthNIST Special Publication 800-52 Revision 2 · n=973,441
Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% Certificate signature uses SHA-256 or stronger: 99.9% 99.9%Certificate signature uses SHA-256 or strongerNIST Special Publication 800-52 Revision 2 · n=973,441
Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% Secure renegotiation is supported: 99.2% 99.2%Secure renegotiation is supportedNIST Special Publication 800-52 Revision 2 · n=973,438
OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% OCSP stapling recommendation is met: 8.3% 8.3%OCSP stapling recommendation is metNIST Special Publication 800-52 Revision 2 · n=973,441
Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% Certificate is publicly trusted: 96.1% 96.1%Certificate is publicly trustedNIST Special Publication 800-52 Revision 2 · n=973,441

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n = 973,441

Most-failed requirement in all ranks: OCSP stapling recommendation is met (NIST Special Publication 800-52 Revision 2).

View as table
RequirementCitationPass sharen
All requirementsNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r23.9%973,441
TLS 1.2 is supportedNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r299.3%973,441
TLS 1.3 is supportedNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r289.5%973,441
SSLv2, SSLv3, TLS 1.0, and TLS 1.1 are disabledNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r263.5%973,441
Forward-secrecy cipher suites are availableNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r299.8%973,441
Obsoleted CBC-only offering is absentNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r227.7%973,441
Certificate public key meets minimum strengthNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r2100%973,441
Certificate signature uses SHA-256 or strongerNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r299.9%973,441
Secure renegotiation is supportedNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r299.2%973,438
OCSP stapling recommendation is metNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r28.3%973,441
Certificate is publicly trustedNIST Special Publication 800-52 Revision 2, Guidelines for TLS Implementations (2019), https://doi.org/10.6028/NIST.SP.800-52r296.1%973,441

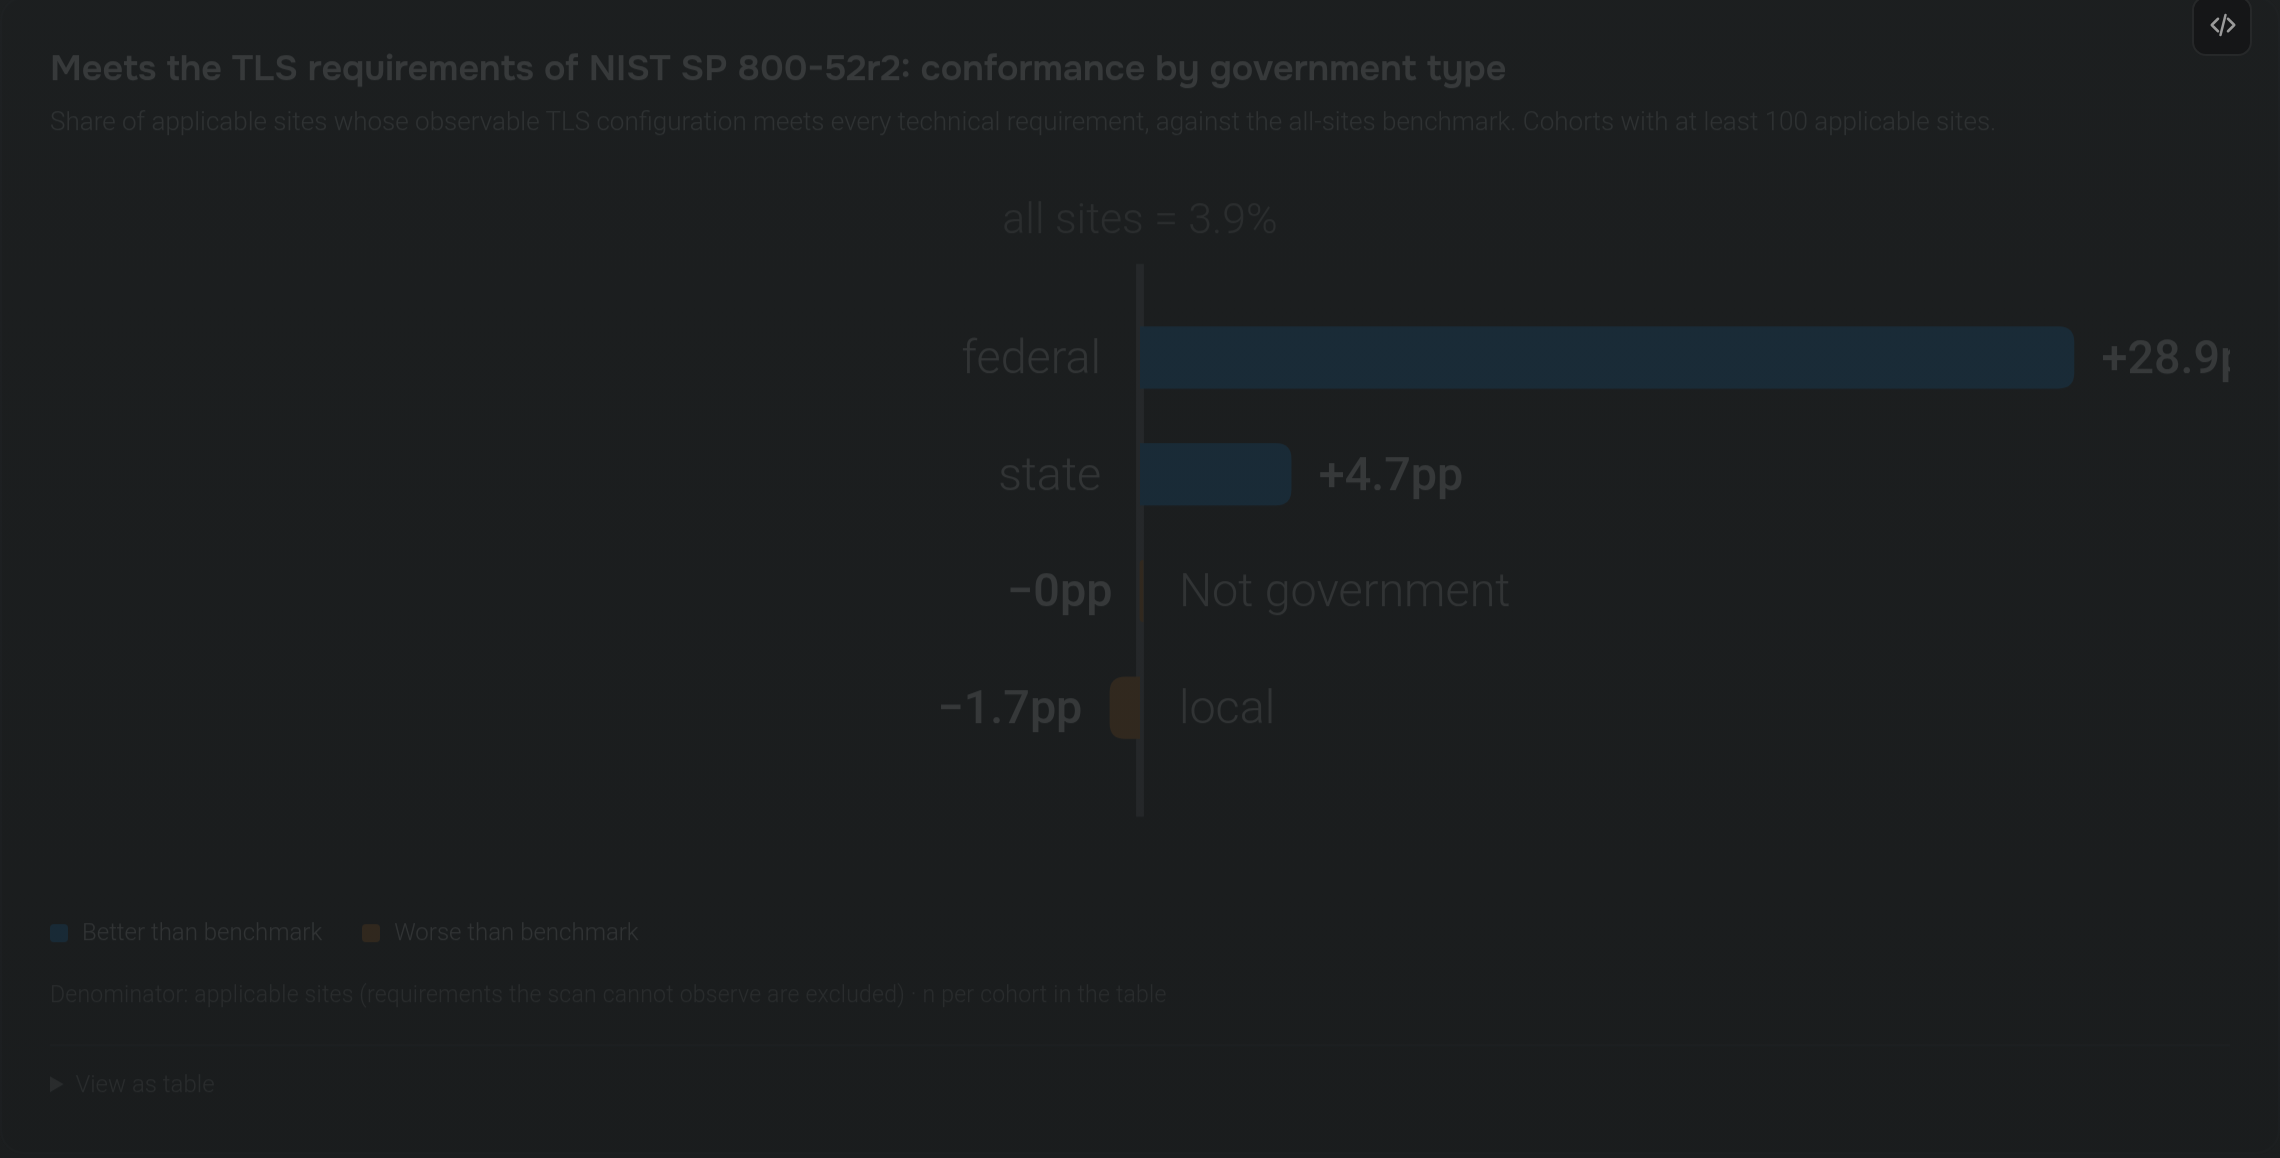
Meets the TLS requirements of NIST SP 800-52r2: conformance by government type

Share of applicable sites whose observable TLS configuration meets every technical requirement, against the all-sites benchmark. Cohorts with at least 100 applicable sites.

all sites = 3.9%federal: 32.8; +28.9pp vs all sites = 3.9% (better); n=531 federal +28.9ppstate: 8.6; +4.7pp vs all sites = 3.9% (better); n=326 state +4.7ppNot government: 3.9; −0pp vs all sites = 3.9% (worse); n=971515 Not government −0pplocal: 2.2; −1.7pp vs all sites = 3.9% (worse); n=1055 local −1.7pp
Better than benchmarkWorse than benchmark

Denominator: applicable sites (requirements the scan cannot observe are excluded) · n per cohort in the table

View as table
govTypeAll requirements metMost-failed requirementn
federal32.8%OCSP stapling recommendation is met531
state8.6%OCSP stapling recommendation is met326
Not government3.9%OCSP stapling recommendation is met971,515
local2.2%OCSP stapling recommendation is met1,055
What drives the failures

The requirements most often missed

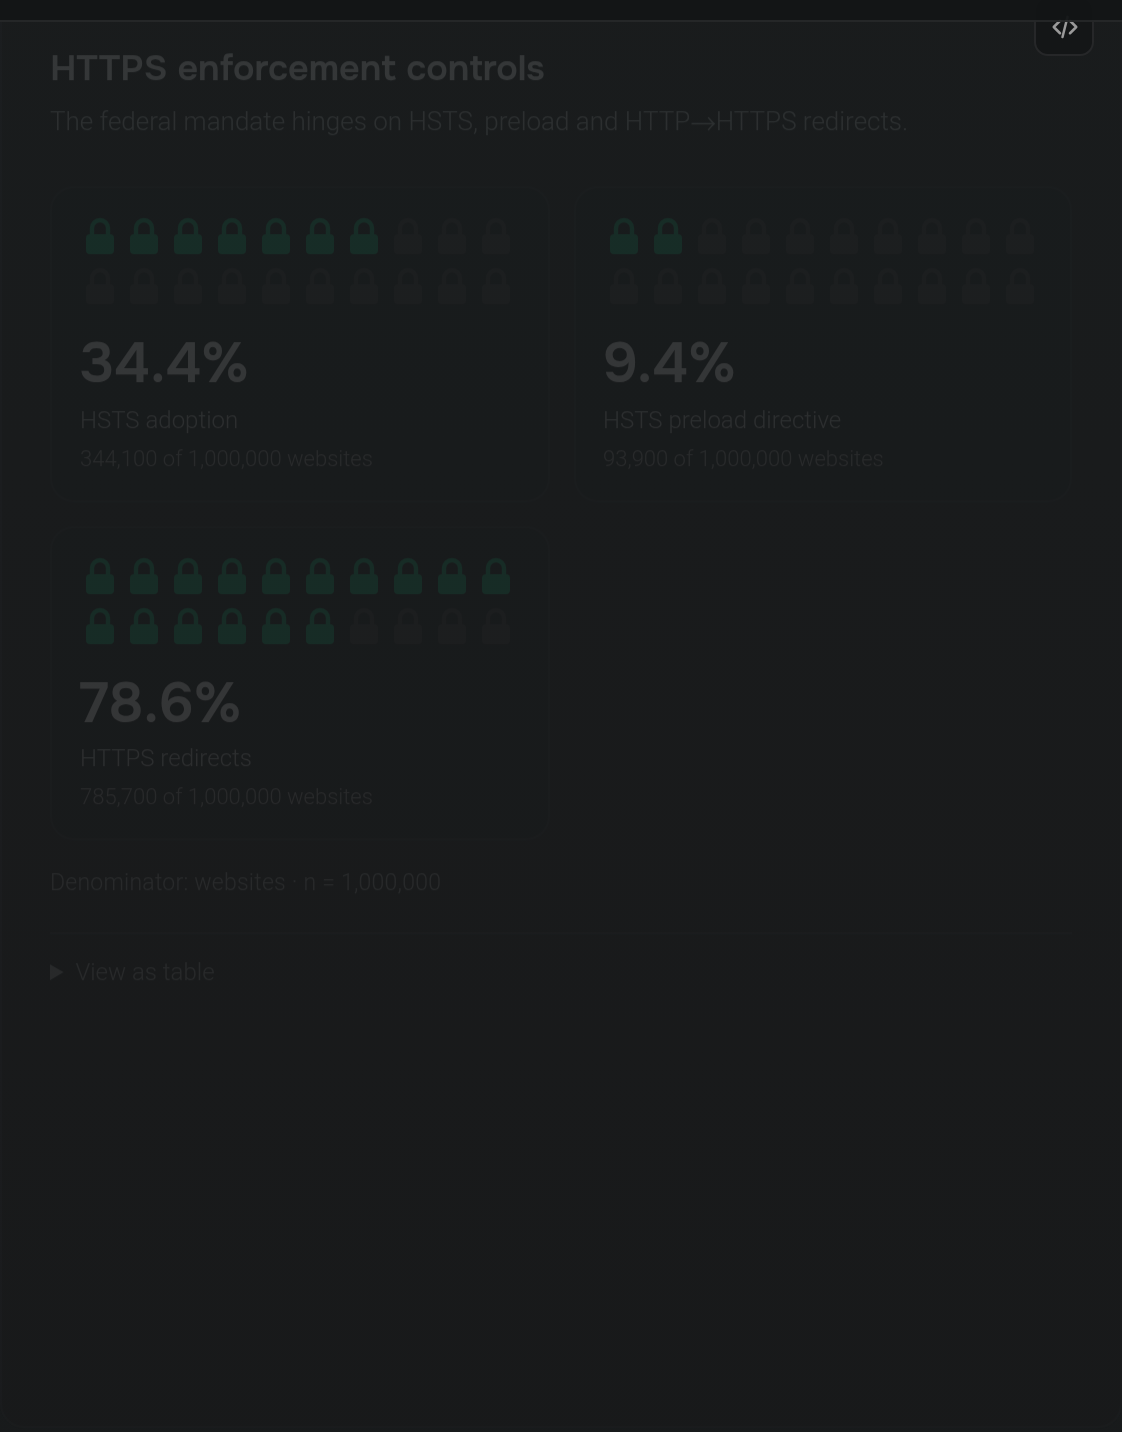
HTTPS enforcement controls

The federal mandate hinges on HSTS, preload and HTTP→HTTPS redirects.

HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% HSTS adoption: 34.4% 34.4%HSTS adoption344,100 of 1,000,000 websites
HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% HSTS preload directive: 9.4% 9.4%HSTS preload directive93,900 of 1,000,000 websites
HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% HTTPS redirects: 78.6% 78.6%HTTPS redirects785,700 of 1,000,000 websites

Denominator: websites · n = 1,000,000

View as table
MeasureShareSitesn
HSTS adoption34.4%344,1001,000,000
HSTS preload directive9.4%93,9001,000,000
HTTPS redirects78.6%785,7001,000,000

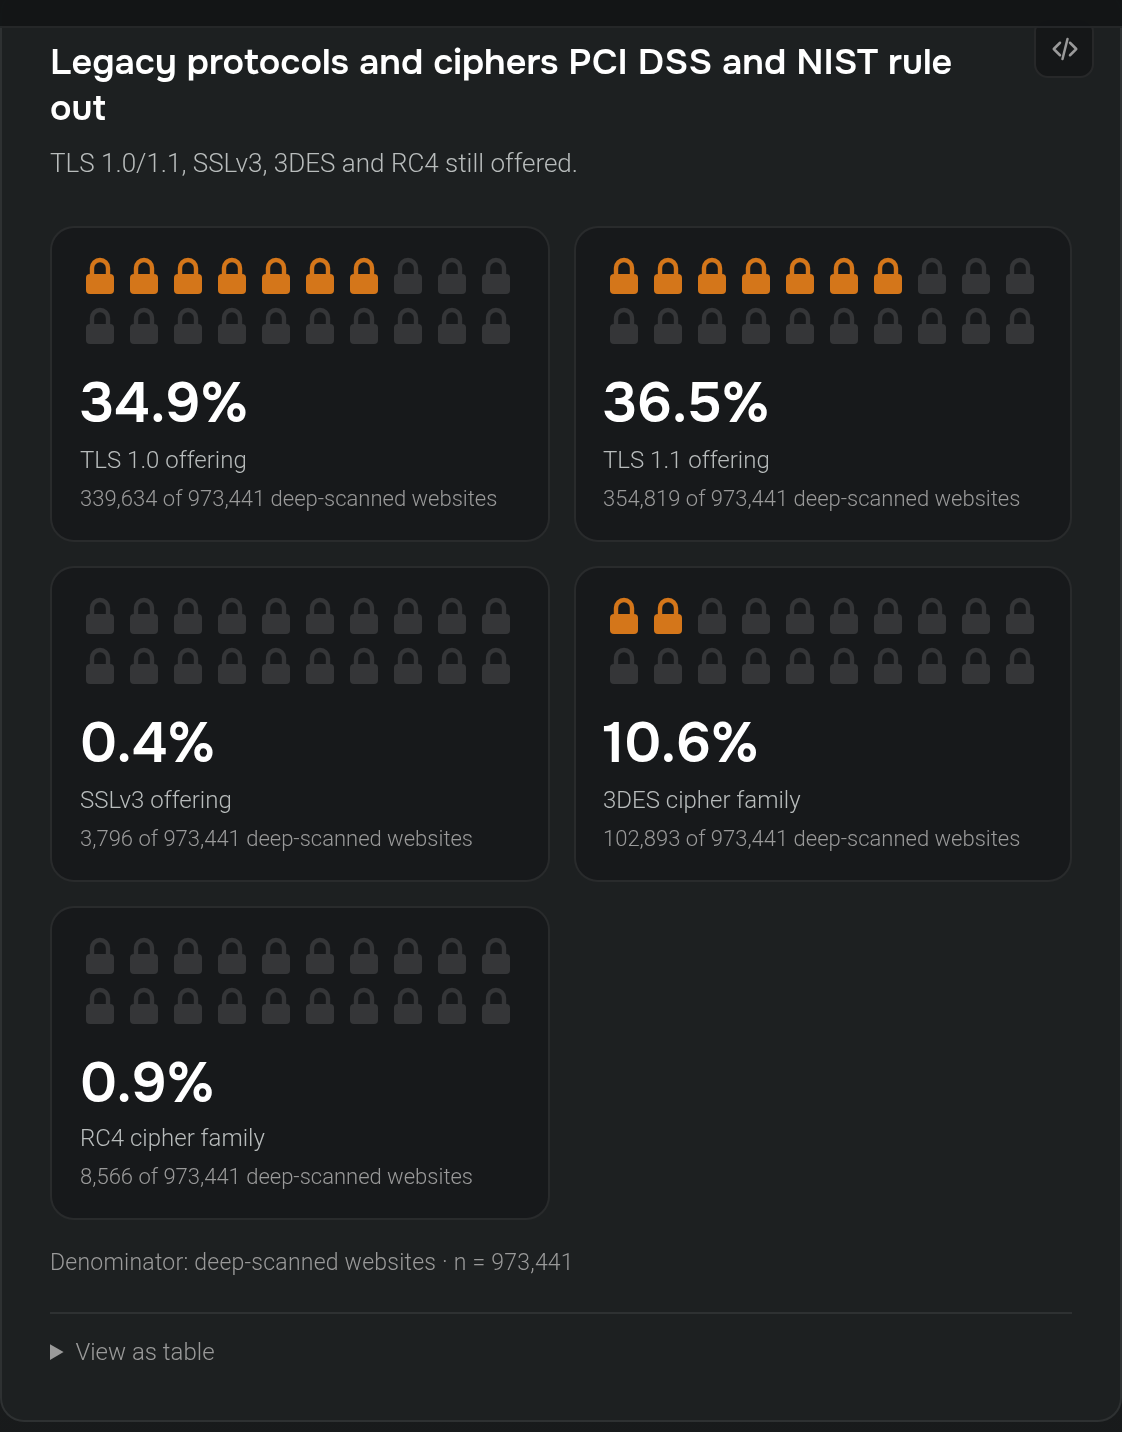
Legacy protocols and ciphers PCI DSS and NIST rule out

TLS 1.0/1.1, SSLv3, 3DES and RC4 still offered.

TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% TLS 1.0 offering: 34.9% 34.9%TLS 1.0 offering339,634 of 973,441 deep-scanned websites
TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% TLS 1.1 offering: 36.5% 36.5%TLS 1.1 offering354,819 of 973,441 deep-scanned websites
SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% SSLv3 offering: 0.4% 0.4%SSLv3 offering3,796 of 973,441 deep-scanned websites
3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 3DES cipher family: 10.6% 10.6%3DES cipher family102,893 of 973,441 deep-scanned websites
RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% RC4 cipher family: 0.9% 0.9%RC4 cipher family8,566 of 973,441 deep-scanned websites

Denominator: deep-scanned websites · n = 973,441

View as table
MeasureShareSitesn
TLS 1.0 offering34.9%339,634973,441
TLS 1.1 offering36.5%354,819973,441
SSLv3 offering0.4%3,796973,441
3DES cipher family10.6%102,893973,441
RC4 cipher family0.9%8,566973,441

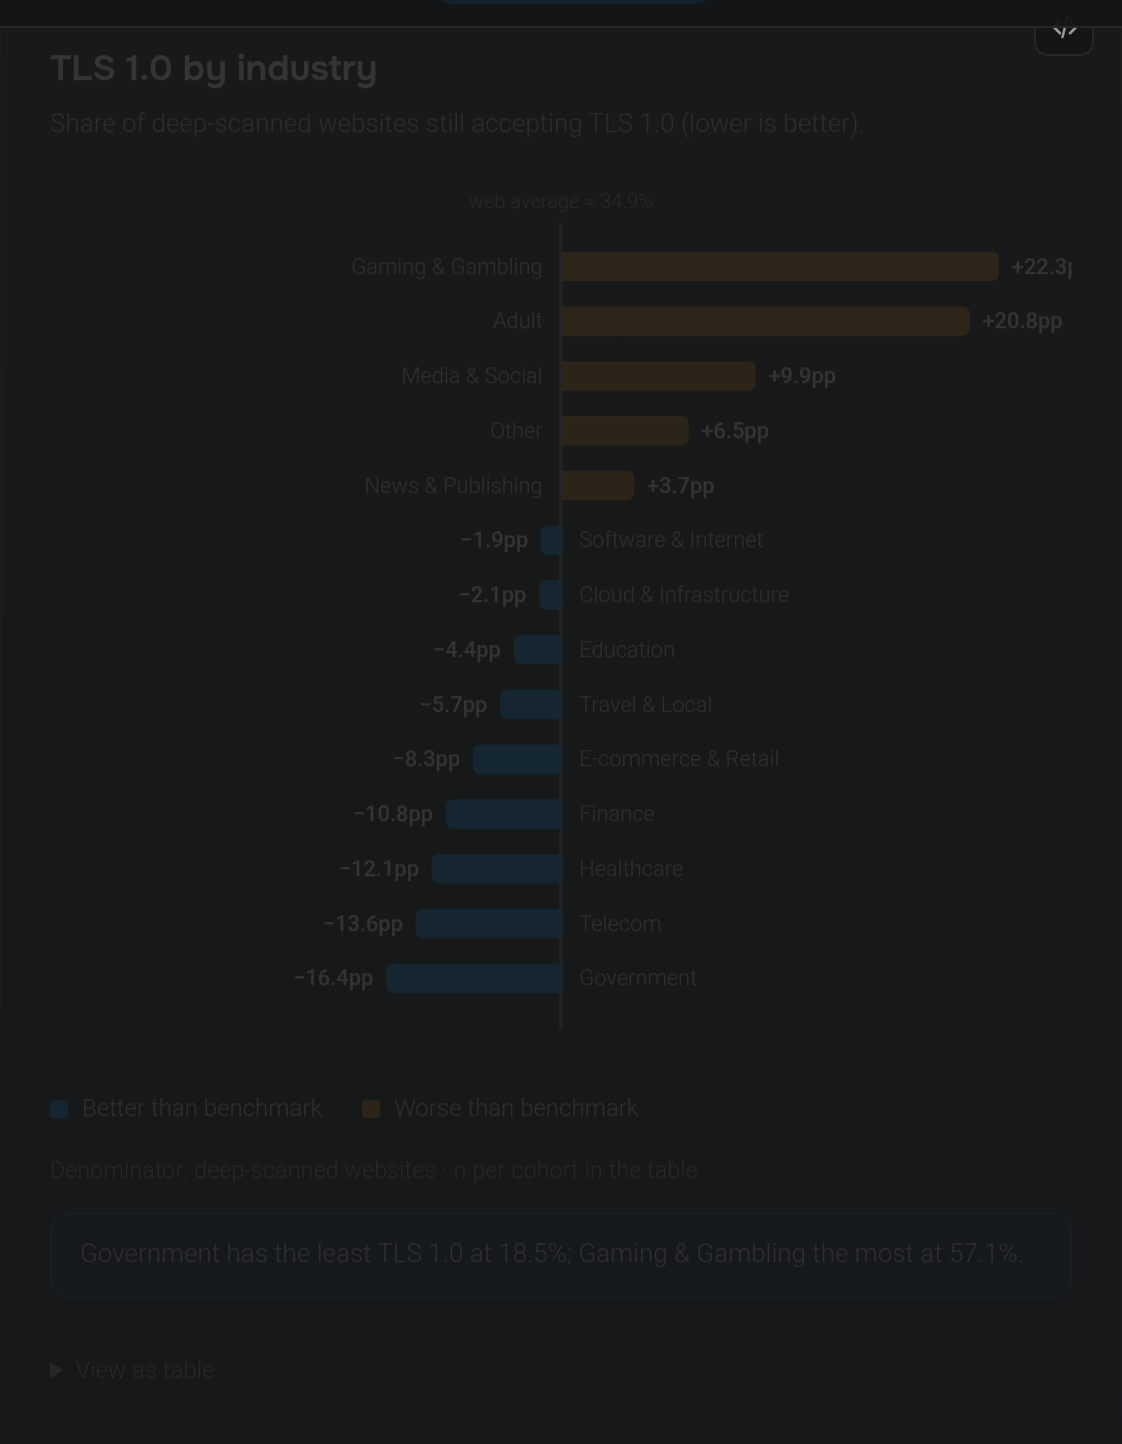
TLS 1.0 by industry

Share of deep-scanned websites still accepting TLS 1.0 (lower is better).

web average = 34.9%Gaming & Gambling: 57.1; +22.3pp vs web average = 34.9% (worse); n=89932 Gaming & Gambling +22.3ppAdult: 55.7; +20.8pp vs web average = 34.9% (worse); n=24873 Adult +20.8ppMedia & Social: 44.8; +9.9pp vs web average = 34.9% (worse); n=120053 Media & Social +9.9ppOther: 41.4; +6.5pp vs web average = 34.9% (worse); n=11457 Other +6.5ppNews & Publishing: 38.6; +3.7pp vs web average = 34.9% (worse); n=34542 News & Publishing +3.7ppSoftware & Internet: 33; −1.9pp vs web average = 34.9% (better); n=221156 Software & Internet −1.9ppCloud & Infrastructure: 32.8; −2.1pp vs web average = 34.9% (better); n=53540 Cloud & Infrastructure −2.1ppEducation: 30.4; −4.4pp vs web average = 34.9% (better); n=102118 Education −4.4ppTravel & Local: 29.2; −5.7pp vs web average = 34.9% (better); n=58256 Travel & Local −5.7ppE-commerce & Retail: 26.6; −8.3pp vs web average = 34.9% (better); n=151466 E-commerce & Retail −8.3ppFinance: 24.1; −10.8pp vs web average = 34.9% (better); n=34232 Finance −10.8ppHealthcare: 22.8; −12.1pp vs web average = 34.9% (better); n=42642 Healthcare −12.1ppTelecom: 21.3; −13.6pp vs web average = 34.9% (better); n=7186 Telecom −13.6ppGovernment: 18.5; −16.4pp vs web average = 34.9% (better); n=21988 Government −16.4pp
Better than benchmarkWorse than benchmark

Denominator: deep-scanned websites · n per cohort in the table

Government has the least TLS 1.0 at 18.5%; Gaming & Gambling the most at 57.1%.

View as table
SliceSharevs benchmarkn
Gaming & Gambling57.1%+22.3pp89,932
Adult55.7%+20.8pp24,873
Media & Social44.8%+9.9pp120,053
Other41.4%+6.5pp11,457
News & Publishing38.6%+3.7pp34,542
Software & Internet33%−1.9pp221,156
Cloud & Infrastructure32.8%−2.1pp53,540
Education30.4%−4.4pp102,118
Travel & Local29.2%−5.7pp58,256
E-commerce & Retail26.6%−8.3pp151,466
Finance24.1%−10.8pp34,232
Healthcare22.8%−12.1pp42,642
Telecom21.3%−13.6pp7,186
Government18.5%−16.4pp21,988
Public sector

Government websites against the web

Not affected by the filter above.

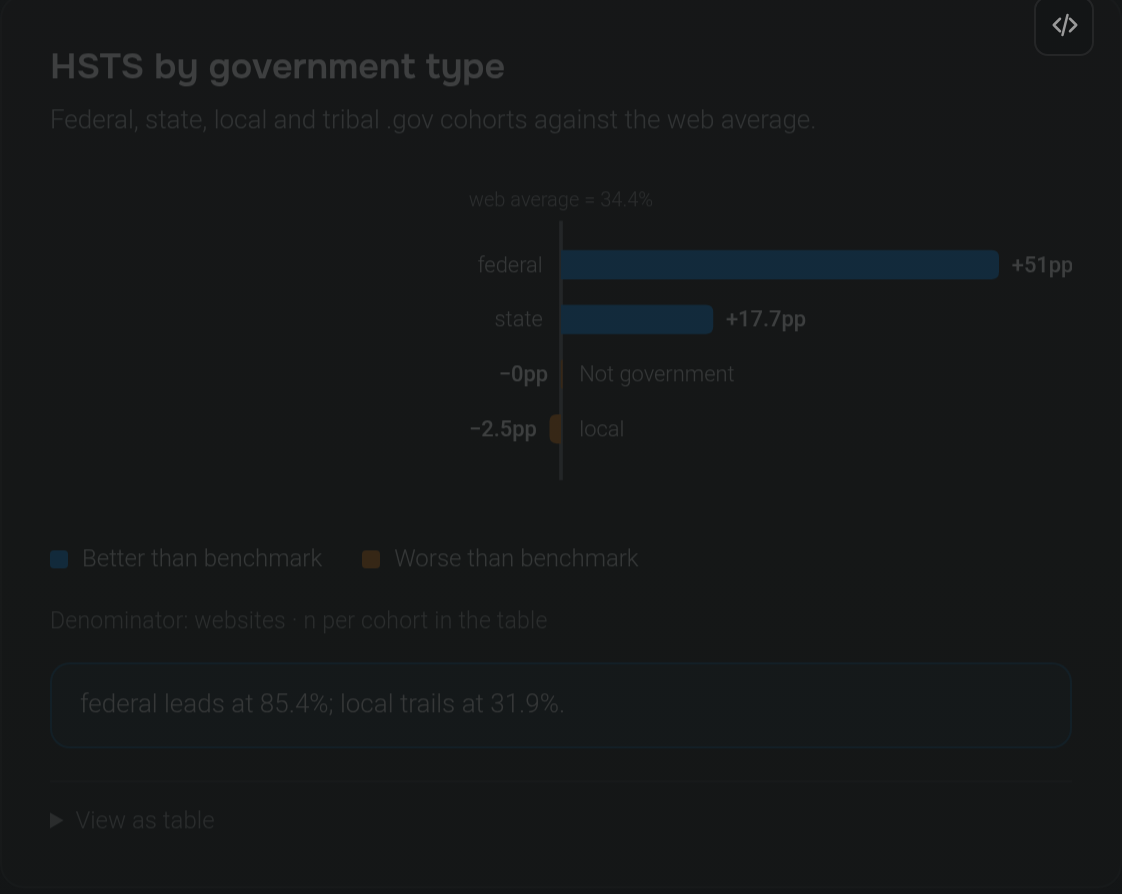
HSTS by government type

Federal, state, local and tribal .gov cohorts against the web average.

web average = 34.4%federal: 85.4; +51pp vs web average = 34.4% (better); n=534 federal +51ppstate: 52.1; +17.7pp vs web average = 34.4% (better); n=330 state +17.7ppNot government: 34.4; −0pp vs web average = 34.4% (worse); n=998061 Not government −0pplocal: 31.9; −2.5pp vs web average = 34.4% (worse); n=1061 local −2.5pp
Better than benchmarkWorse than benchmark

Denominator: websites · n per cohort in the table

federal leads at 85.4%; local trails at 31.9%.

View as table
SliceSharevs benchmarkn
federal85.4%+51pp534
state52.1%+17.7pp330
Not government34.4%−0pp998,061
local31.9%−2.5pp1,061

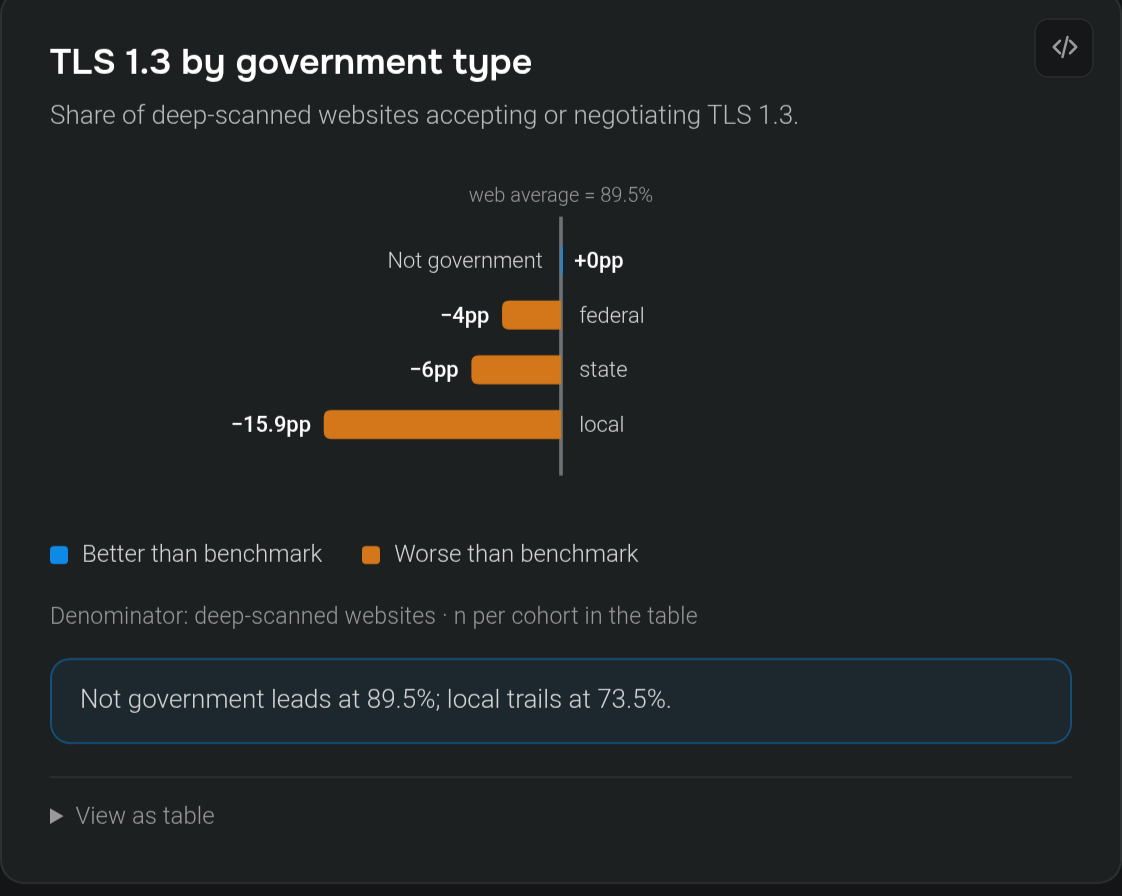
TLS 1.3 by government type

Share of deep-scanned websites accepting or negotiating TLS 1.3.

web average = 89.5%Not government: 89.5; +0pp vs web average = 89.5% (better); n=971515 Not government +0ppfederal: 85.5; −4pp vs web average = 89.5% (worse); n=531 federal −4ppstate: 83.4; −6pp vs web average = 89.5% (worse); n=326 state −6pplocal: 73.5; −15.9pp vs web average = 89.5% (worse); n=1055 local −15.9pp
Better than benchmarkWorse than benchmark

Denominator: deep-scanned websites · n per cohort in the table

Not government leads at 89.5%; local trails at 73.5%.

View as table
SliceSharevs benchmarkn
Not government89.5%+0pp971,515
federal85.5%−4pp531
state83.4%−6pp326
local73.5%−15.9pp1,055

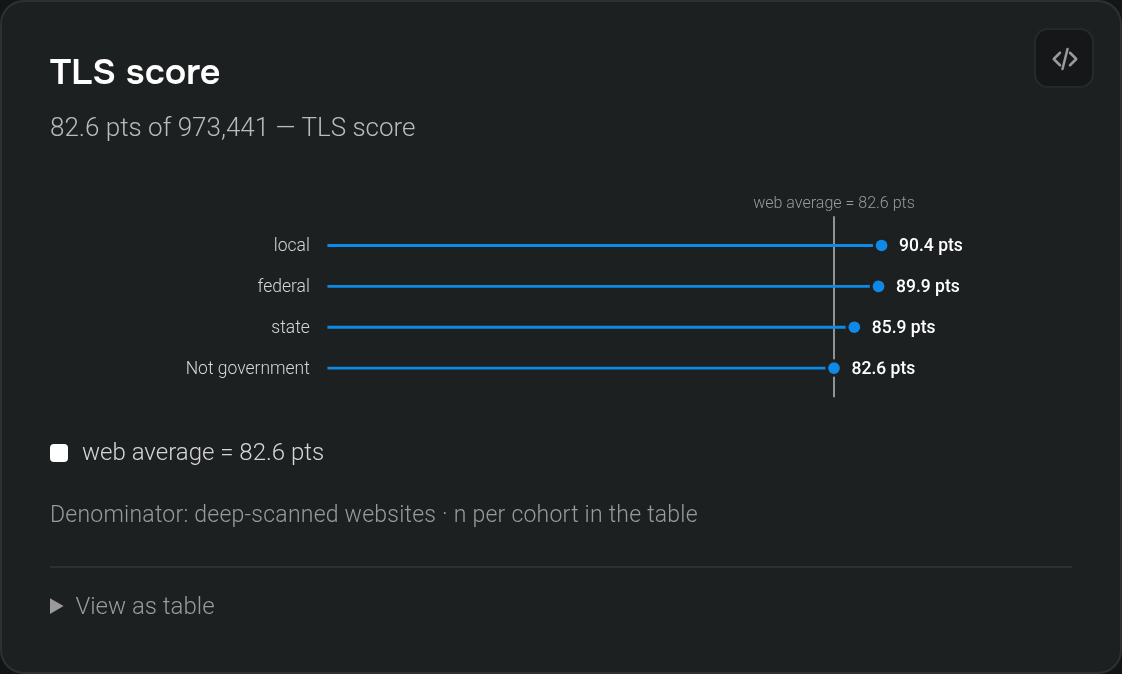
TLS score

82.6 pts of 973,441 — TLS score

web average = 82.6 ptslocal: TLS score 90.4 pts; n=1,055local90.4 ptsfederal: TLS score 89.9 pts; n=531federal89.9 ptsstate: TLS score 85.9 pts; n=326state85.9 ptsNot government: TLS score 82.6 pts; n=971,515Not government82.6 pts
web average = 82.6 pts

Denominator: deep-scanned websites · n per cohort in the table

View as table
CohortAverage scorevs benchmarkn
local90.4 pts+7.8 pts1,055
federal89.9 pts+7.3 pts531
state85.9 pts+3.3 pts326
Not government82.6 pts−0 pts971,515
Loading...